Date: Wednesday, December 9, 2026
Time: 12:00pm ET
CPE: 1.0
This session will explore the rapidly evolving role of artificial intelligence in government and the implications for audit, risk management, internal controls, and governance. Panelists representing the audit and oversight community, public accounting/consulting, federal agencies, and state and local government will share perspectives on AI risks, governance frameworks, control considerations, and practical approaches for providing assurance over the use of AI.
Learning Objective:
- Identify key risks associated with the use of AI in government operations and decision-making.
- Describe governance and internal control considerations for the responsible implementation and use of AI.
- Evaluate approaches for auditing AI-related risks and controls, including data reliability, cybersecurity, transparency, and accountability.
- Recognize emerging practices for incorporating AI-related risks into audit planning and risk assessments.
Moderator
George Fallon – RMA Associates LLC
George Fallon is an IT Director at RMA Associates, where he leads the firm’s cybersecurity practice and supports federal agencies in securing and modernizing their information technology environments. With more than 30 years of federal IT audit and cybersecurity experience, George has built and led teams conducting technical assessments of networks, servers, databases, cloud platforms, and complex web applications. George began his career with a major accounting firm and has since led cybersecurity and penetration testing teams supporting some of the federal government’s largest and most complex organizations. George is recognized for translating highly technical findings into clear, actionable information for executive and technical audiences. A published author and frequent presenter, George regularly shares insights on cybersecurity and emerging technology risks. His current focus is advancing Zero Trust Architecture across the federal landscape. George is a CPA, CISA, CDPSE, CISSP, CGFM, and CEH
Presenter
Dr. Brett Baker (former Federal Inspector General)
Dr. Brett Baker is a nationally recognized federal oversight leader and retired Inspector General. He served as the Inspector General of the National Archives and Records Administration (2021–2025) and dual-hatted as the Acting Inspector General for the Commodity Futures Trading Commission (2023–2024). Over his 35 year career, he held senior audit executive roles at the NRC, DoD, NSF, Commerce, DFAS, and Education, and is a U.S. Army veteran. Dr. Baker chaired the CIGIE Audit Committee (2024–2025) and led the Federal Audit Executive Council for many years. Dr. Baker is a frequent national speaker, with 175 presentations, and is a recipient of the Presidential Rank Award (Meritorious Executive), the AGA Elmer Staats Award, and the JFMIP Scantlebury Award. He holds a doctorate and master’s degree in information technology management, as well as bachelor’s degrees in accounting and sociology. He is also a CPA, CISA, and Fellow of the National Academy of Public Administration.
Presenter
Megan Gaillard, CPA, CGFM, CFE, CIA, CGAP, CRMA, and CISA, Collier County Board of County Commissioners
Megan Gaillard serves as an auditor and consultant with Auditing, Forensics, and Consulting, LLC where she completes government special reviews for financial and budget information. Megan has extensive experience in internal audit, forensic auditing, fraud examination, internal controls, and government oversight. Her previous roles include the Division Director for Corporate Compliance and Continuous Improvement at the Collier County Board of County Commissioners; Interim City Auditor and Quality Control Audit Manager for the City of Fort Lauderdale; and Director of Audit for the Palm Beach County Office of Inspector General, where audits identified more than $24 million in questioned, identified, and avoidable costs. Megan also teaches graduate-level courses in accounting information systems and forensics. She is a CPA, CGFM, CFE, CIA, CGAP, CRMA, and CISA and holds bachelor’s and master’s degrees in accounting from Florida Gulf Coast University.
Presenter
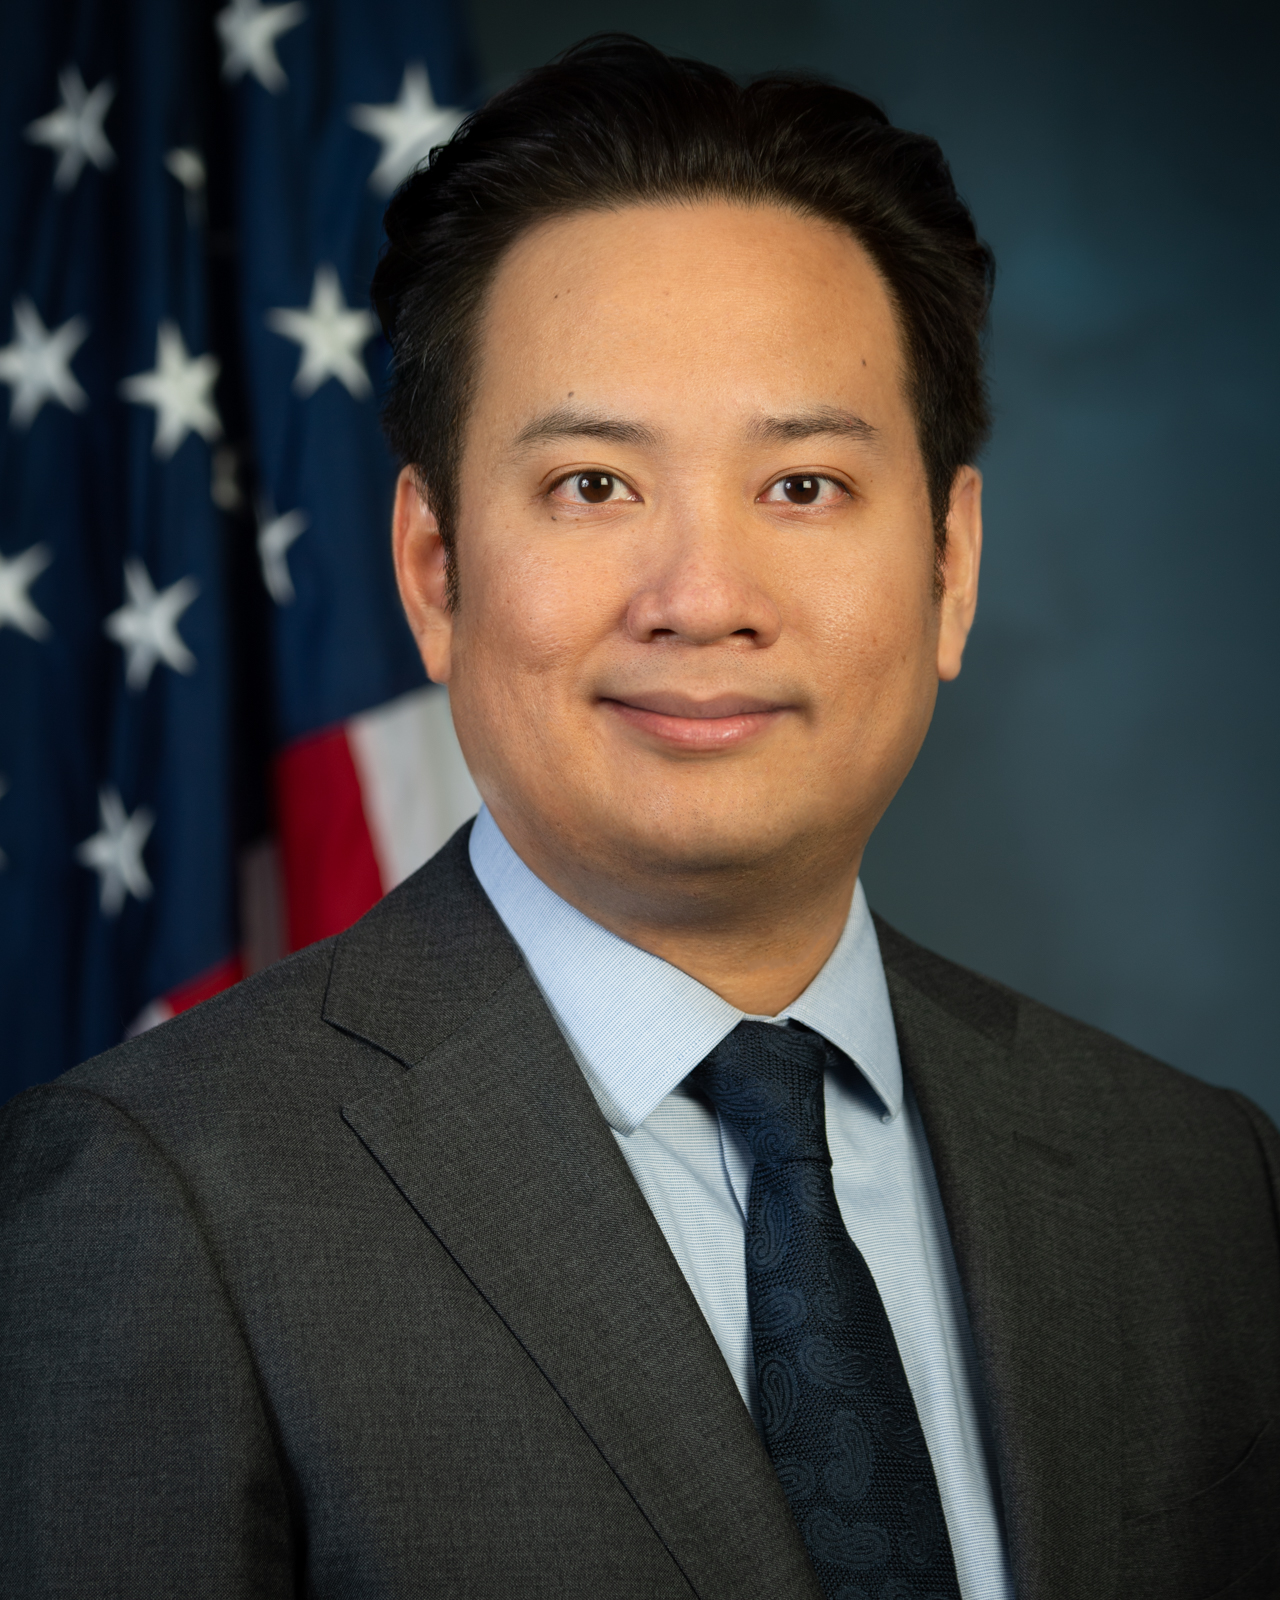
Dan Lam, Director, Financial Systems Quality Assurance Division, at the U.S. Department of Housing and Urban Development
Dan Lam is a Federal information security and financial systems leader with 16+ years safeguarding HUD’s core, mission-critical financial systems. As an Information System Security Officer and Privacy Liaison Officer, he leads continuous monitoring and compliance across HUD’s financial systems cybersecurity, and privacy portfolio — spanning NIST SP 800-53, FISMA, FedRAMP, the Privacy Act, and FFMIA/OMB Circular A-123. Mr. Lam’s recent work sits at the intersection of fraud prevention, improper-payment reduction, and enterprise risk management. He and his team have led HUD’s rollout of the government-wide Do Not Pay initiative under Executive Order 14249 (Protecting America’s Bank Account Against Fraud, Waste, and Abuse) and OMB M-25-32 — coordinating across Treasury, HUD program offices, and oversight bodies to build durable, department-wide safeguards against improper and fraudulent payments. The effort stood up automated payment-verification processes and Treasury data-sharing/API connectivity, produced updated HUD enterprise policy that closed longstanding audit findings, and advanced HUD’s payment-integrity posture well ahead of federal deadlines. Mr. Lam’s broader record includes a substantial Authorization to Operate portfolio, the migration of legacy financial systems into secure cloud environments, and a shift from reactive to proactive monitoring through automation and emerging technology — work that helped resolve long-standing material weaknesses and contribute to a clean audit opinion. A recognized voice on security, privacy, and enterprise risk, he regularly advises executive leadership and interagency partners. Mr. Lam holds an MS in Information Systems Technology Management from George Washington University, a BS in General Science from the University of Oregon, and a CISSP certification.